Companies preparing for the May 2027 deadline for complete compliance with India’s DPDP Act will need to examine how personal data moves through their networks, business processes and artificial intelligence systems. The compliance work is expected to extend beyond databases and conventional access controls to include automated workflows, AI agents and the tools connected to them.
Consent changes must reach every system
Yashdeep Vaishnav, regional vice president and country manager for India at enterprise automation company UiPath, said that organisations must first establish clear visibility over personal-data flows. That means identifying the people, systems, automations and AI agents that can access or process the information.
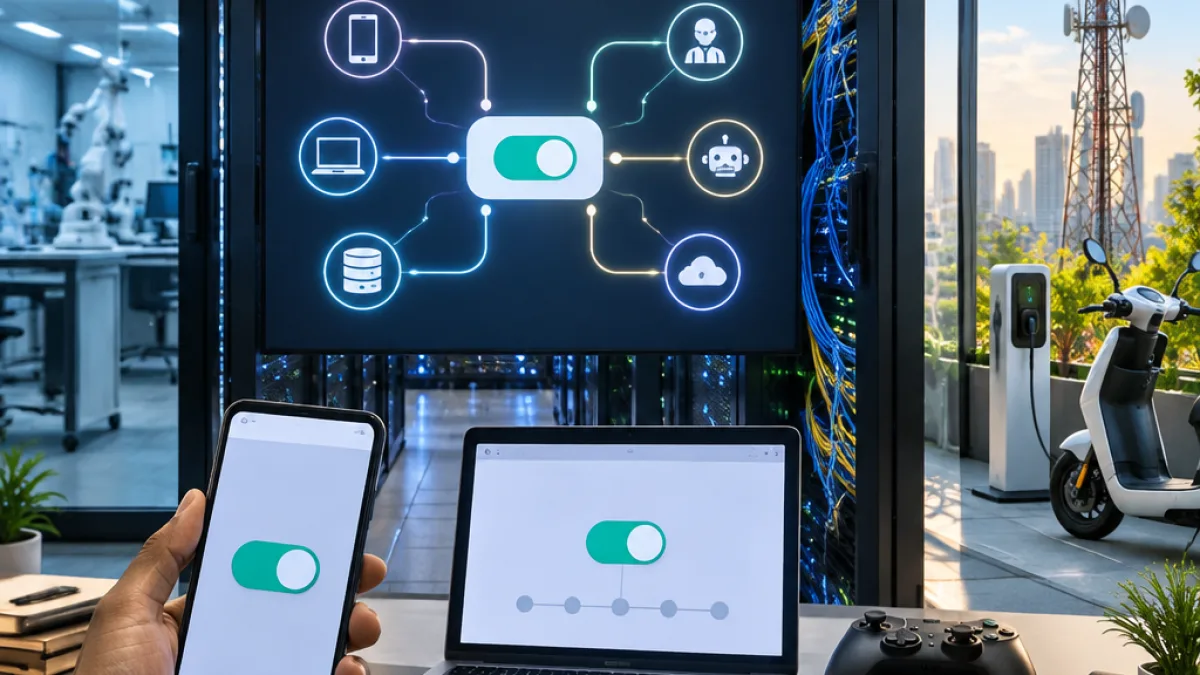
A key requirement will be ensuring that a customer’s decision to change or withdraw consent is reflected throughout the organisation. If a consent status changes, the update must reach every process that depends on it rather than remaining limited to the application where the change was made. This could affect automated decisions, background workflows and AI-powered services that continue operating after the original interaction with a customer.
- Data mapping: Companies need to identify where personal data moves and who or what can access it.
- Consent enforcement: Changes and withdrawals must be applied across dependent systems and processes.
- AI oversight: Human supervision should be built into automated operations as a standard control.
AI expands the privacy perimeter
Pankaj Thapa, co-founder and chief executive officer of cybersecurity company Mirror Security, said privacy safeguards must cover the full AI-processing chain. This includes prompts submitted to an AI system, information retrieved for an answer, an agent’s retained memory, its outputs and the external tools it can access.
As organisations deploy more AI agents, the number of routes through which information can be accessed or disclosed also increases. Thapa pointed to risks involving excessive data access, information leakage and unauthorised disclosure. For companies, this means that an AI system cannot be assessed only by checking the database or application it uses; its surrounding integrations and automated actions also require scrutiny.
Governance will need evidence
Vaishnav said human oversight protocols should be the default for automated operations, rather than a safeguard activated only when a problem occurs. He described a division in which AI agents handle reasoning, automation carries out tasks and people remain responsible for leadership and control. In this approach, governance is built into the design of business processes instead of being treated as a separate compliance activity.
Arnab Chattopadhyay, co-founder of agentic AI penetration-testing platform FireCompass, said organisations should reassess weaknesses in their networks and address them before they are discovered. Once the DPDP Act is fully applicable, companies will need to demonstrate not only how they respond to cyberattacks but also whether their internal policies were adequate and whether evidence of those policies can be produced.
The compliance deadline therefore places emphasis on documentation as well as technical controls. Businesses will need to know how data is handled across conventional software and AI-enabled operations, while maintaining proof that consent, oversight and security practices are being applied across those environments.